Showing posts with label deeplearning. Show all posts

Monday, November 9, 2026

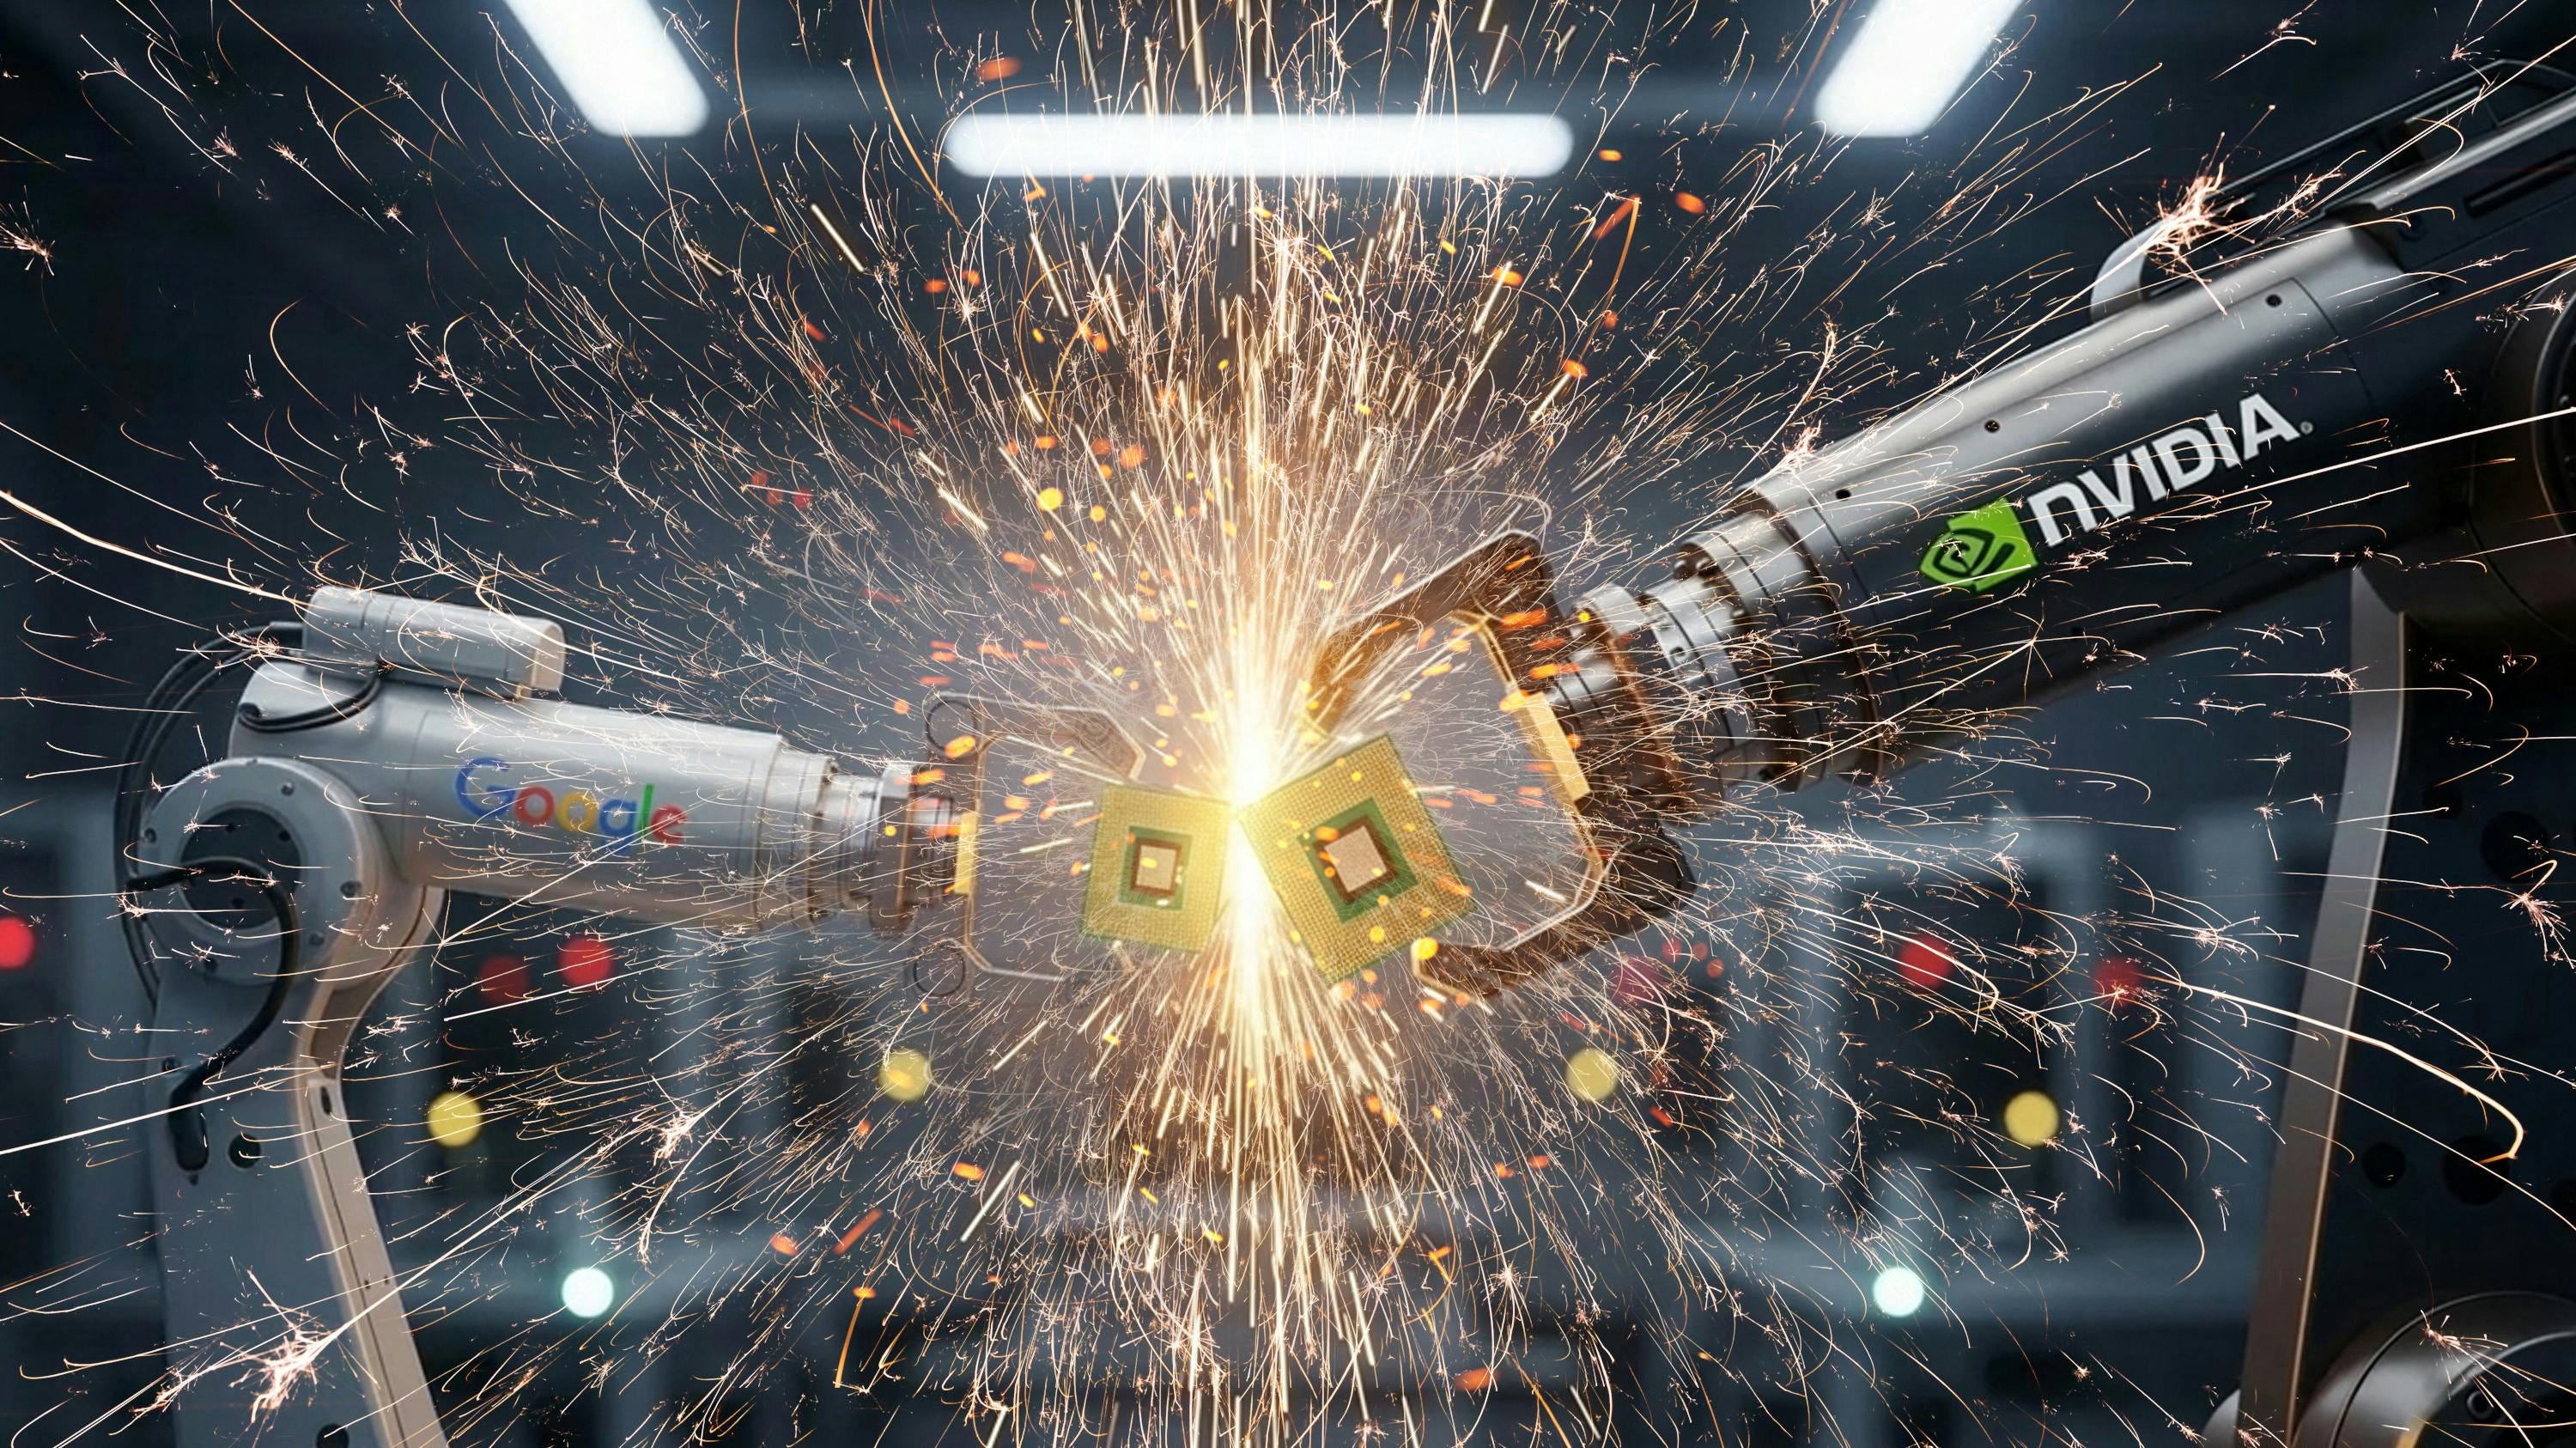
Google Escalates Nvidia Rivalry With New Versions of Its TPU Systems

Alphabet Inc.’s Google is rolling out a broader array of artificial intelligence chips, aiming to capitalize on its rapid ascent as a challenger to Nvidia Corp. in a market worth hundreds of billions of dollars. The company is introducing two new variations of its tensor processing units, or TPUs, custom-made semiconductors that help develop and run AI software. The latest chips will address the need for confidential computing and help models access a wider range of information when handling queries. More broadly, they’re meant to serve an industry that’s shifting toward the use of AI agents and confronting security challenges……..Continue reading….

Source: Bloomberg.

.

Critics:

Nvidia is a software and fabless company which designs and supplies graphics processing units (GPUs), application programming interfaces (APIs) for data science and high-performance computing, as well as system on a chip units (SoCs) for the mobile computing and automotive market. Nvidia’s specialization means it is able to charge a premium for its products.

In fact, its chips, which are manufactured in Taiwan, are so unique that companies looking to build AI capabilities are complaining that there is a shortage of them. The ownership structure of Nvidia (NVDA) stock is a mix of institutional, retail and individual investors. Approximately 35.48% of the company’s stock is owned by Institutional Investors, 3.93% is owned by Insiders and 60.59% is owned by Public Companies and Individual Investors.
According to supply chain data estimates from Bloomberg, Arcuri is spot on with Microsoft being Nvidia’s largest customer. Nvidia stock fell sharply Tuesday, trading at its lowest level since late May as the market awaits Big Tech earnings and looks at potential competition in AI hardware. Nvidia shares closed down 7% at $103.73. The tech-heavy Nasdaq Composite Index dropped 1.3%.

The top individual shareholders of Nvidia are Jen-Hsun (“Jensen”) Huang, Mark A. Stevens, and Tench Coxe. The top institutional shareholders are Vanguard Group Inc., BlackRock Inc. (BLK), and FMR LLC. Nvidia stock has gained 3,776% since the start of 2019 as the company benefits from selling the main chip necessary for artificial intelligence work, minting many new multimillionaires in the process.

The main issue is that Nvidia’s graphics processing units, even its popular H100s, don’t have enough memory to handle the immense amount of video data needed to train these models, founders of AI video startups tell me. Nvidia designs and manufactures GPUs for gaming, cryptocurrency mining, and professional applications, as well as chip systems for use in vehicles, robotics, and other tools.

Today, data center processors for analytics and AI have quickly become Nvidia’s largest source of revenue, surpassing the company’s historical main business line of GPUs (graphic processing units). Nvidia Overtakes Microsoft as World’s Most Valuable Company Nvidia Overtakes Microsoft as World’s Most Valuable Company. Nvidia has become the most valuable company in the world after its market capitalization grew to $3.34 trillion, overtaking Microsoft at $3.32.

 In 2023, companies like Meta, Oracle, and Microsoft signaled their interest in AMD GPUs as a more cost-effective solution and a way to avoid a potential vendor lock-in with dominant Nvidia. AMD’s Instinct MI300 series, for example, is considered a viable alternative for scientific computing and AI uses. Concerns over Nvidia’s valuation seems to be the chief reason behind recent heavy selling. Even now, Nvidia shares on an elevated forward price-to-earnings (P/E) ratio of 43.6 times.

This remains far ahead of an average of 25.5 times for S&P 500 shares. Bank of America analyst Vivek Arya noted Nvidia is one of the firm’s top “rebound” picks amid what he expects to be a comeback for semiconductors to end 2024. “Our base case remains for a [semiconductor] rebound likely in Q4 as seasonal headwinds dissipate,” Arya wrote in a note to clients.

World’s most important fuel of the AI frenzy, NVIDIA, is facing accusations of acting as a “GPU cartel” and controlling supply in the data center market, according to statements made by executives at rival chipmaker Groq and former AMD executive Scott Herkelman. Reports claiming that Nvidia (NASDAQ:NVDA) is buying Xbox from Microsoft (NASDAQ:MSFT) have been debunked as an April Fool’s Day prank from TweakTown.

The “Nvidia buys Xbox” post spread online and started trending on some social media websites. A $20,000 investment made in the semiconductor giant 10 years ago would be worth more than $3.4 million today — up by around 170 times in value. It is also worth noting that the company has taken less than a decade to turn a $20,000 investment into precisely a $1 million.

The ownership structure of Nvidia (NVDA) stock is a mix of institutional, retail and individual investors. Approximately 35.48% of the company’s stock is owned by Institutional Investors, 3.93% is owned by Insiders and 60.59% is owned by Public Companies and Individual Investors.
The AI Chip Behind Nvidia’s Supersonic Stock RallyBNN Bloomberg 22:14 
.
TensorProcessingUnits ,TPUs ,Nvidia, GoogleTech,ArtificialIntelligence, ,MachineLearning ,DeepLearning ,DataScience ,AIProcessing ,NeuralNetworks ,ThinkDeep ,ComputePower ,TechInnovation ,FutureOfTech ,AIHardware ,BigData ,ArtificialNeuralNetworks ,TechTrends ,ProcessedWithTPUs ,AcceleratedComputing ,SmartTech ,CloudComputing

Sunday, November 1, 2026

Looking For Reliable AI? Enkrypt Identifies Safest LLMs With New Tool

Venturebeat made with DALL-E

In the age of generative AI, the safety of large language models (LLMs) is just as important as their performance at different tasks. Many teams already realize this and are pushing the bar on their testing and evaluation efforts to foresee and fix issues that could lead to broken user experiences, lost opportunities and even regulatory fines. But, when models are evolving so quickly in both open and closed-source domains, how does one determine which LLM is the safest to begin with? Well, Enkrypt has the answer: a LLM Safety Leaderboard.…..Story continues…..

Source:  VentureBeat

.

Critics:

A backdoor in a computer system, a cryptosystem, or an algorithm, is any secret method of bypassing normal authentication or security controls. These weaknesses may exist for many reasons, including original design or poor configuration. Due to the nature of backdoors, they are of greater concern to companies and databases as opposed to individuals.

Backdoors may be added by an authorized party to allow some legitimate access, or by an attacker for malicious reasons. Criminals often use malware to install backdoors, giving them remote administrative access to a system. Once they have access, cybercriminals can “modify files, steal personal information, install unwanted software, and even take control of the entire computer.”

Backdoors can be very hard to detect, and are usually discovered by someone who has access to the application source code or intimate knowledge of the operating system of the computer. Denial of service attacks (DoS) are designed to make a machine or network resource unavailable to its intended users.

Attackers can deny service to individual victims, such as by deliberately entering a wrong password enough consecutive times to cause the victim’s account to be locked, or they may overload the capabilities of a machine or network and block all users at once. While a network attack from a single IP address can be blocked by adding a new firewall rule, many forms of Distributed denial of service (DDoS) attacks are possible, where the attack comes from a large number of points.

In this case defending against these attacks is much more difficult. Such attacks can originate from the zombie computers of a botnet or from a range of other possible techniques, including distributed reflective denial of service (DRDoS), where innocent systems are fooled into sending traffic to the victim.

With such attacks, the amplification factor makes the attack easier for the attacker because they have to use little bandwidth themselves. To understand why attackers may carry out these attacks, see the ‘attacker motivation’ section. A direct-access attack is when an unauthorized user (an attacker) gains physical access to a computer, most likely to directly copy data from it or to steal information.

Attackers may also compromise security by making operating system modifications, installing software worms, keyloggers, covert listening devices or using wireless microphones. Even when the system is protected by standard security measures, these may be bypassed by booting another operating system or tool from a CD-ROM or other bootable media. Disk encryption and Trusted Platform Module are designed to prevent these attacks.

Direct service attackers are related in concept to direct memory attacks that allows an attacker to gain direct access to a computer’s memory. The attacks “take advantage of a feature of modern computers that allow certain devices, such as external hard drives, graphics cards or network cards, to access the computer’s memory directly.”

To help prevent these attacks, computer users must ensure that they have a strong passwords, that their computer is locked at all times when they are not using it, and that they keep their computer with them at all times when traveling. Eavesdropping is the act of surreptitiously listening to a private computer conversation (communication), usually between hosts on a network.

It typically occurs when a user connects to a network where traffic is not secured or encrypted and sends sensitive business data to a colleague, which when listened to by an attacker could be exploited. Data transmitted across an “open network” allows an attacker to exploit a vulnerability and intercept it via various methods.

Unlike malware, direct-access attacks, or other forms of cyber attacks, eavesdropping attacks are unlikely to negatively affect the performance of networks or devices, making them difficult to notice.In fact, “the attacker does not need to have any ongoing connection to the software at all. The attacker can insert the software onto a compromised device, perhaps by direct insertion or perhaps by a virus or other malware, and then come back some time later to retrieve any data that is found or trigger the software to send the data at some determined time.”

Using a virtual private network (VPN), which encrypts data between two points, is one of the most common forms of protection against eavesdropping. Using the best form of encryption possible for wireless networks is best practice, as well as using HTTPS instead of an unencrypted HTTP.

Programs such as Carnivore and NarusInSight have been used by the Federal Bureau of Investigation (FBI) and NSA to eavesdrop on the systems of internet service providers. Even machines that operate as a closed system (i.e., with no contact with the outside world) can be eavesdropped upon by monitoring the faint electromagnetic transmissions generated by the hardware. TEMPEST is a specification by the NSA referring to these attacks.

Malicious software (malware) is any software code or computer program “intentionally written to harm a computer system or its users.” Once present on a computer, it can leak sensitive details such as personal information, business information and passwords, can give control of the system to the attacker, and can corrupt or delete data permanently.

Another type of malware is ransomware, which is when “malware installs itself onto a victim’s machine, encrypts their files, and then turns around and demands a ransom (usually in Bitcoin) to return that data to the user.

Surfacing in 2017, a new class of multi-vector, polymorphic cyber threats combine several types of attacks and change form to avoid cybersecurity controls as they spread. Multi-vector polymorphic attacks, as the name describes, are both multi-vectored and polymorphic. Firstly, they are a singular attack that involves multiple methods of attack.

In this sense, they are “multi-vectored (i.e. the attack can use multiple means of propagation such as via the Web, email and applications.” However, they are also multi-staged, meaning that “they can infiltrate networks and move laterally inside the network. The attacks can be polymorphic, meaning that the cyberattacks used such as viruses, worms or trojans “constantly change (“morph”) making it nearly impossible to detect them using signature-based defences.

How To Budget In Uncertain Times

GETTY It’s that time of the year again… time to create next year’s budget. Budgeting in the best of times is difficult, and now it’s even mo...